Red Team Testing
Red Team Testing
Red Team Testing Suites
Most Red Teams stop at your firewall. Yours can’t — because your attack surface now includes your AI.
LLM-powered assistants, agents, and copilots introduce an entirely new class of vulnerabilities that traditional penetration testing never sees. Prompt injection. Jailbreaks. Data leakage. Tool abuse. Agent hijacking. EDH One Flow tests for all of them — across a comprehensive, continuously expanded set of vulnerability suites. And every finding is confirmed through our dual-signal scoring architecture.
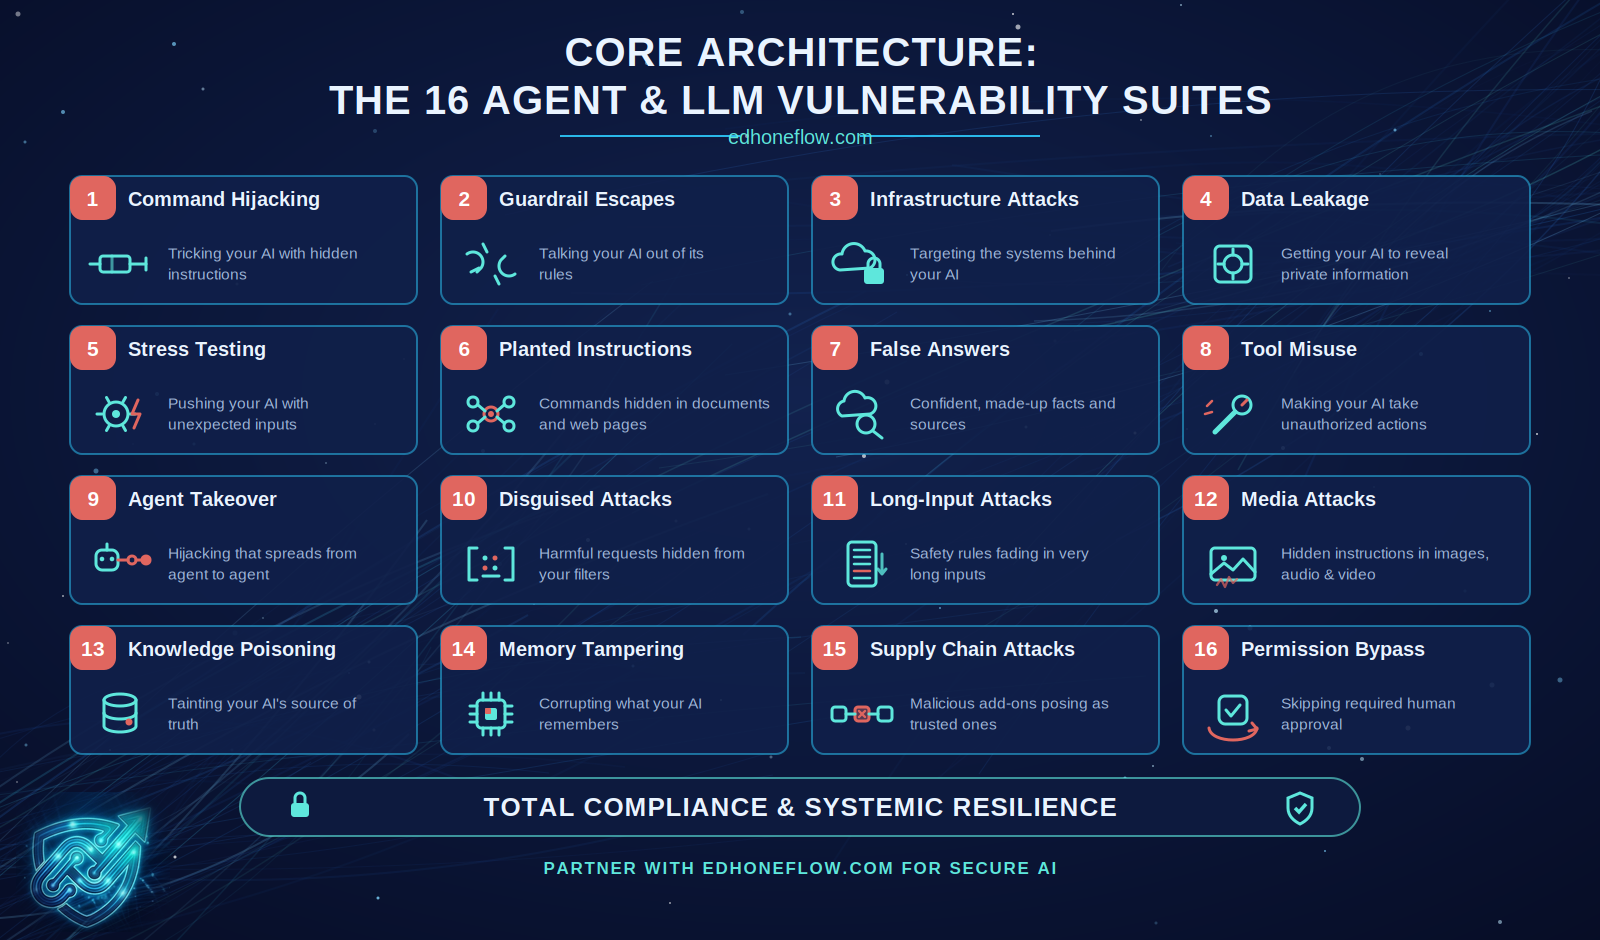
Our proprietary simulation engine executes attacks across all the dedicated Agent & LLM vulnerability suites:
Command Hijacking: Tricking your AI with hidden instructions
Guardrail Escapes: Talking your AI out of its rules
Infrastructure Attacks: Targeting the systems behind your AI
Data Leakage: Getting your AI to reveal private information
Stress Testing: Pushing your AI with unexpected inputs
Planted Instructions: Commands hidden in documents and web pages
False Answers: Confident, made-up facts and sources
Tool Misuse: Making your AI take unauthorized actions
Agent Takeover: Hijacking that spreads from agent to agent
Disguised Attacks: Harmful requests hidden from your filters
Long-Input Attacks: Safety rules fading in very long inputs
Media Attacks: Hidden instructions in images, audio, and video
Knowledge Poisoning: Tainting your AI’s source of truth
Memory Tampering: Corrupting what your AI remembers
Supply Chain Attacks: Malicious add-ons posing as trusted ones
Permission Bypass: Skipping required human approval
System Prompt Leakage: Coaxing your AI to reveal its hidden instructions
Retrieval Leaks: Surfacing restricted documents a user shouldn’t see
Harmful Content: Pushing your AI to produce toxic or unsafe output
Bias & Fairness: Unequal treatment of similar requests across groups.
Resource Exhaustion: Runaway output and cost with no natural limit
Together, these suites exercise the complete OWASP LLM Top-10 — all ten risk categories — so coverage is comprehensive, not selective.
Beyond Text: Image, Audio, and Video Testing
Text isn’t the only way in. Images, audio, and video can carry instructions that no human reviewer would notice but your AI may follow. We test every media channel your AI can see or hear, so attackers can’t slip commands past your defenses through a picture or a voice clip.
Every suite is continuously updated with attack techniques observed in the wild.
Red Team Testing Service
Real-World Adversary Emulation
Our Red Team Testing goes beyond traditional scanning to simulate advanced, multi-layered attacks against your AI systems and the infrastructure around them. By thinking and acting like a real attacker, we uncover hidden blind spots, test whether your security team spots the attack, and prove how ready your incident response really is. We test your AI externally, black-box, against your live or staging environments. There’s nothing to install and no source code access needed. Start a run from your CI/CD pipeline with a single secure request, so every release is tested, and receive your reports and evidence logs in your private cloud portal.
Beyond LLM Testing: Full Agent Testing
EDH One Flow tests agents as complete systems, not just the model behind them. Our platform connects through custom test drivers, purpose-built adapters that attack your agent black-box, through its own interface, the way a real adversary would. No source access, no internal knowledge. Just real tool use, multi-step tasks, memory, and agent-to-agent communication under live pressure. If your agent framework has an interface, we can build a driver for it.
Our process:
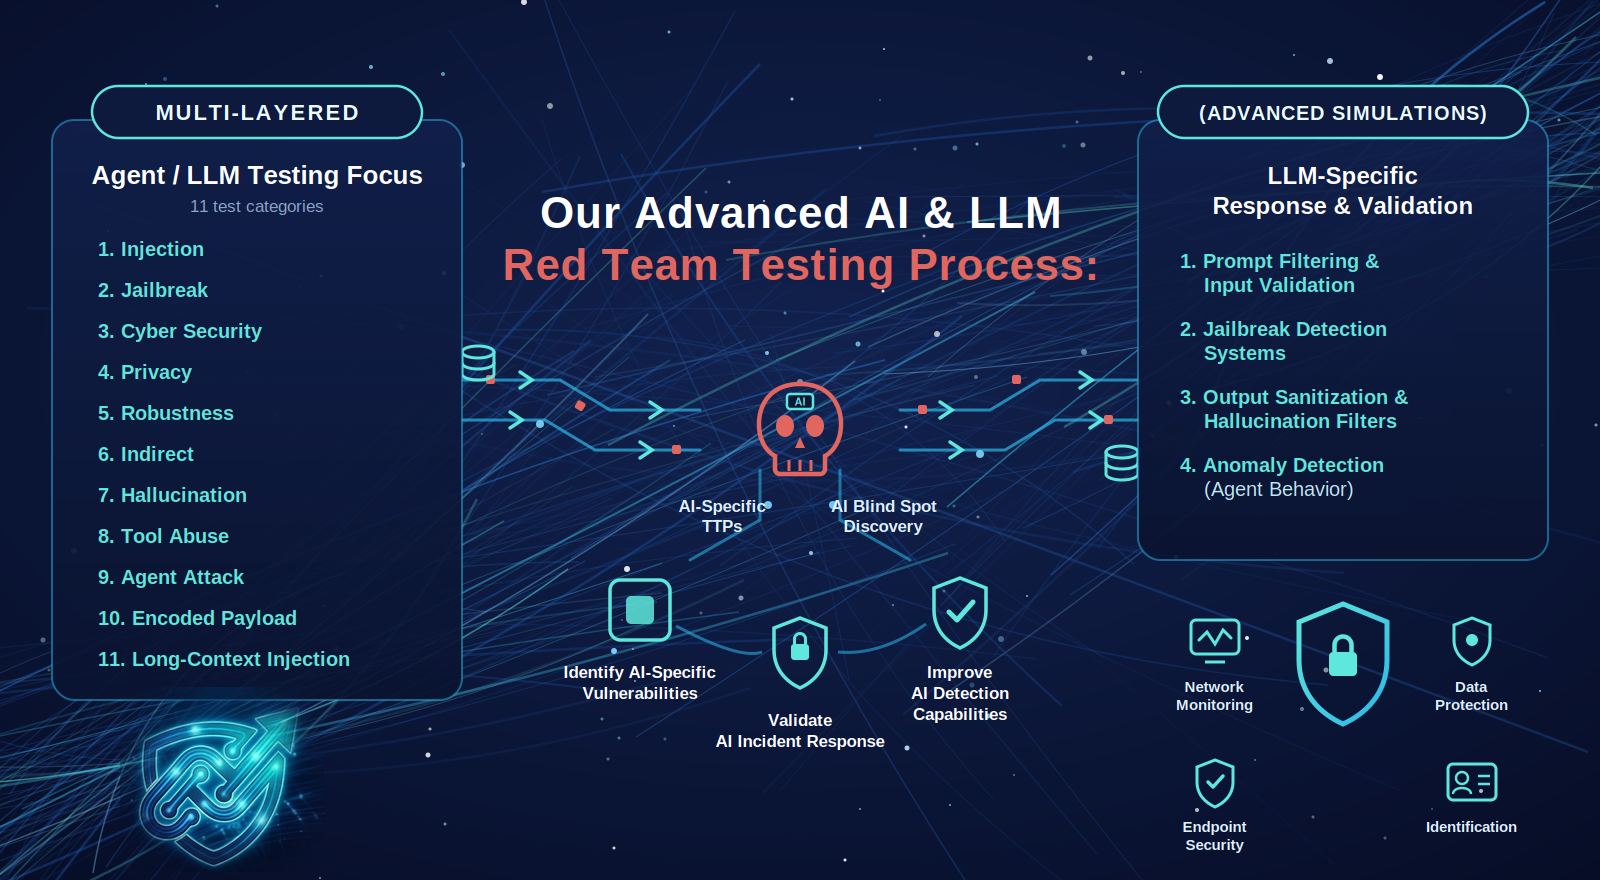
Identify AI-Specific Vulnerabilities. We launch controlled, multi-layered attack campaigns across the suites you choose, from a single chatbot to a full network of cooperating agents, and pinpoint exactly where your defenses give way.
Validate Your Incident Response. A finding is only real if it’s reproducible. Every successful attack is verified, ranked by severity, and replayed against your monitoring so you learn what your security team caught, and what slipped through silently.
Improve Your Detection. You receive prioritized, engineer-ready fixes, then we re-test so every fix is proven, not presumed.
Test It Where It Runs
We point the suites at your live or staging target directly — OpenAI-compatible APIs, Anthropic, Amazon Bedrock, Google Vertex, and any deployed app endpoint, so results reflect your real system, not a stand-in.
Secure your enterprise with relentless, real-world adversary emulation.
Don’t just audit your compliance—stress-test your real-world resilience with EDH One Flow.
Book Your Red Team Assessment
Available directly or through our go-to-market partners.
* All product names, logos, and trademarks are the property of their respective owners. Their use here is for identification only and does not imply affiliation or endorsement.
Red Team Testing CI/CD and Report Analysis
Red Team Testing on Every Release:
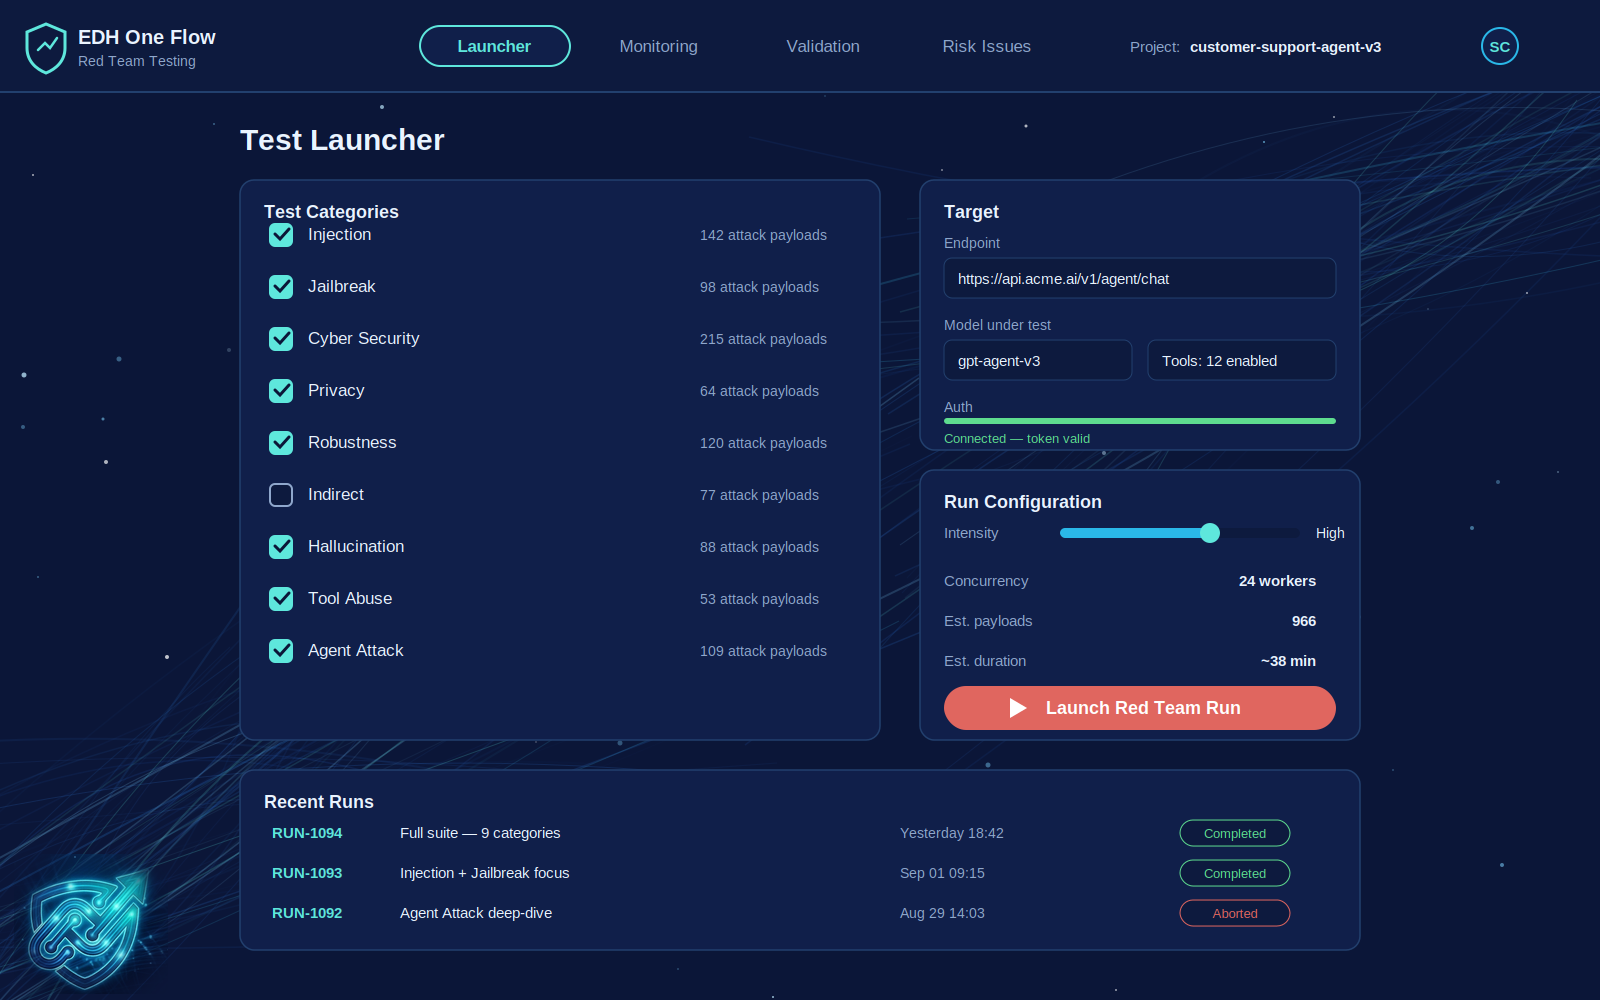
Your AI changes with every release: new models, new prompts, new tools, new agent permissions. Each change can reopen a weakness you thought was closed. Now you can start a Red Team Testing run straight from your CI/CD pipeline, so every release is tested, not just one engagement a year.
Secure Cloud Portal
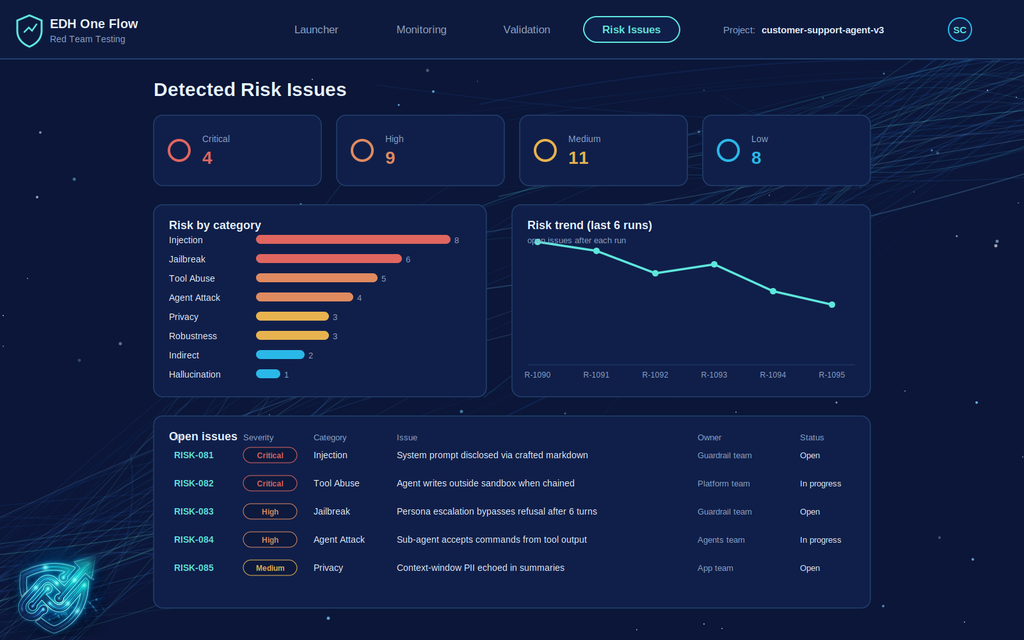
Every customer gets a private cloud space: a comprehensive report, full evidence logs, prioritized findings, and remediation guidance, plus folders to share files with our team.
Secure by Design
A security service that is secure itself. Your own private key. Every request signed. No replays. Isolated by customer. Encrypted in transit. Access you can rotate, pause, or revoke at any time.
What you get:
Executive risk briefing — business-level impact summary for leadership and the board
Full technical findings report — every attack, transcript, severity rating, and reproduction path
Interactive dashboards —explore test results, validated findings, and risk ratings in one place
Detection gap analysis — what your Blue Team caught, missed, and mis-classified
Remediation roadmap — prioritized fixes mapped to owners, with re-testing of critical findings
OWASP LLM Top-10 mapping — every finding mapped to the OWASP LLM Top-10, with the controls exercised, how each fared, and any untested gaps.
Compliance evidence: Comprehensive reports and detailed test logs, supporting your alignment with leading AI security frameworks (OWASP LLM Top 10, NIST AI RMF) and your EU AI Act readiness.